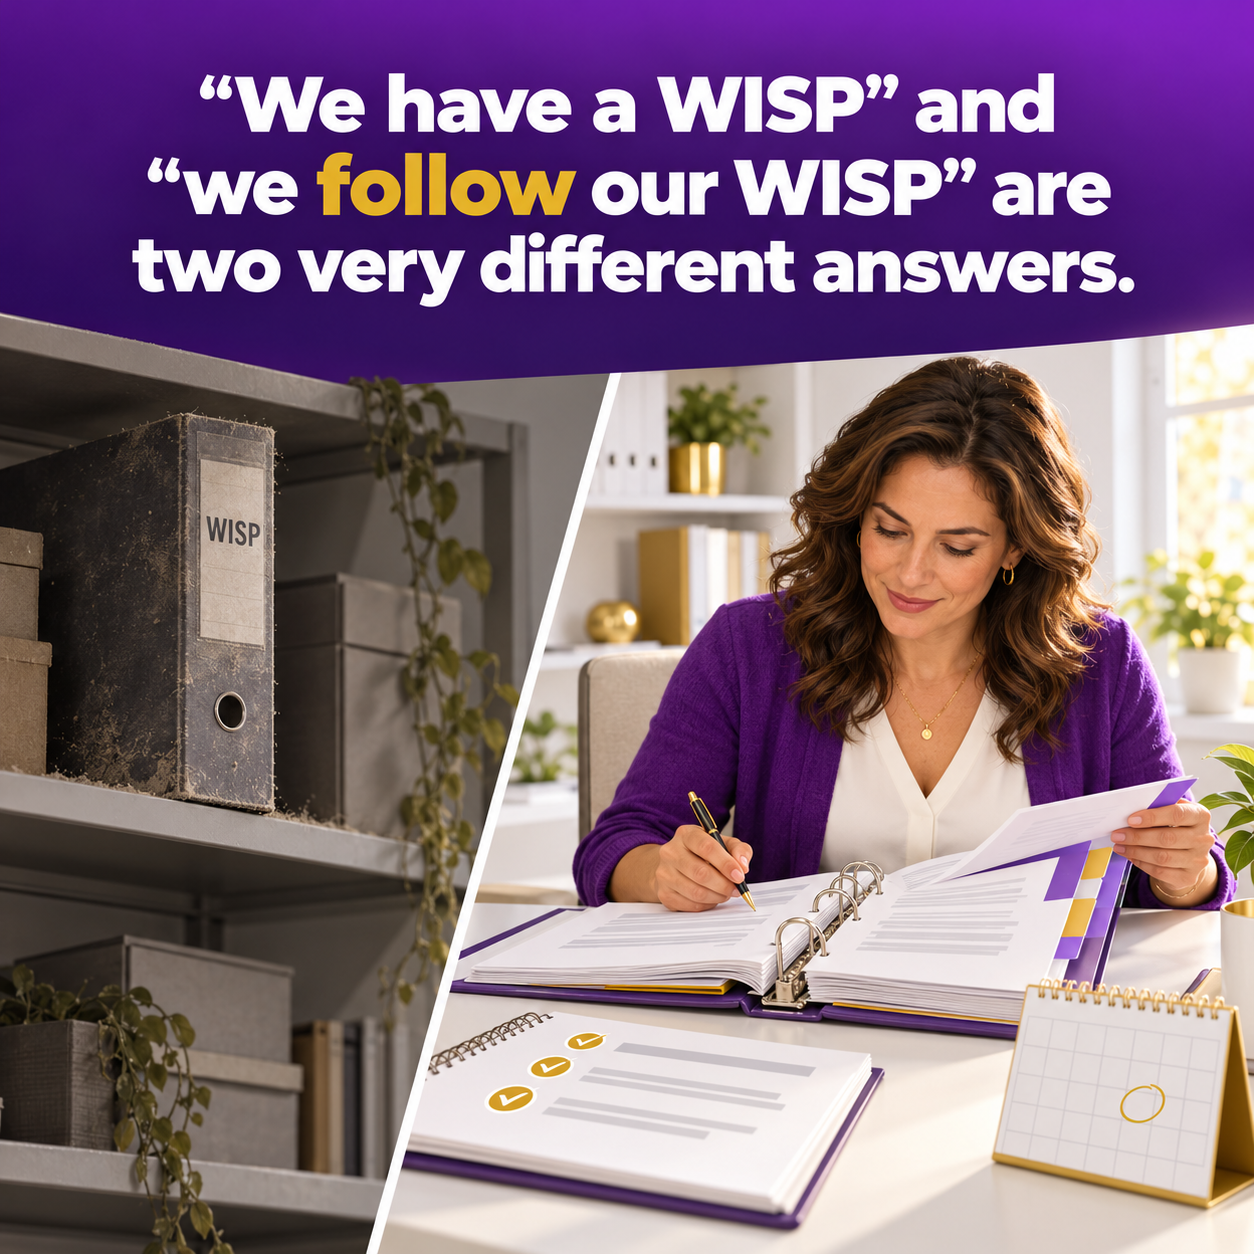
Ask most Florida insurance agency owners whether they have a Written Information Security Program, and many will say yes. Somewhere in a shared drive or a filing cabinet, there is a document with that title on it.
Ask a follow-up question, such as when it was last reviewed, who is responsible for each section, or where the training records are, and the confidence often fades. That gap between having a WISP and following a WISP is where agencies get into trouble.
What a WISP Is Supposed to Be
A Written Information Security Program describes how your agency protects the customer information entrusted to it. Florida Administrative Code Rule 69O-128.032 expects licensees to maintain a comprehensive written program with administrative, technical, and physical safeguards appropriate to the size and complexity of the agency and the sensitivity of the information it handles.
In plain terms, a WISP should answer a few basic questions. What information do you hold? What could go wrong? What are you doing about it? Who is responsible? How do you know it is working?
The key word is program. A program is something you run, not something you file.
Why So Many WISPs Become Shelfware
The pattern is remarkably consistent. An agency downloads a template, fills in the name, signs it, and puts it away. Over time, the document drifts further and further from reality. Common signs include:
• Policies that reference software, vendors, or devices the agency stopped using years ago
• A designated security contact who no longer works there
• Training requirements with no record that training ever happened
• An incident response section nobody on staff has read
• No record of any review since the original signature date
A WISP like this may look fine sitting in a folder. It does not hold up well when a regulator, a carrier, or a cyber insurer asks you to show how it works in practice.
What "Following Your WISP" Actually Looks Like
An agency that follows its WISP can produce evidence. Not perfection, just proof that the program is alive.
It reflects reality
The policies describe the systems, vendors, and workflows your agency uses today. If you switched agency management systems or moved files to the cloud, the WISP says so.
Someone owns it
A specific person is responsible for the program overall, and responsibilities for key areas such as access control, training, and vendor oversight are clearly assigned.
It has a risk assessment behind it
The safeguards in your WISP should connect to an actual assessment of the risks your agency faces. That assessment should be revisited periodically and whenever something significant changes.
It produces records
Training sign-offs, access reviews, backup restore tests, vendor reviews, and incident logs are all evidence that the program is operating. These records are often more valuable than the policy document itself.
It gets reviewed
At least once a year, and after major changes such as a new system, an office move, or a security incident, the WISP is reviewed and updated. Each review is dated and documented.
The Sections That Matter Most
Every agency's WISP will look a little different, but strong programs usually address:
• Designation of the person responsible for the program
• Risk assessment and how often it is updated
• Access controls, including onboarding and offboarding procedures
• Multi-factor authentication and password standards
• Employee training and awareness
• Oversight of service providers who handle customer information
• Backup and recovery
• Incident response and breach notification
• Physical security of the office and devices
• Secure disposal of records and equipment
The View From the Carrier Side
I spent years working inside a specialty insurance carrier before founding Main Event Managed Services. One lesson from that side of the industry stuck with me: when something goes wrong, the questions focus on what was actually done, not what was written down. A policy that says employees receive annual training means very little without a record that they did.
That perspective shapes how we help agencies. The goal is not a thicker binder. The goal is a program your team actually runs, with evidence that builds naturally over time.
Getting Your WISP Back on Track
If your WISP has been sitting untouched, the fix is very manageable:
• Pull out the current document and read it end to end
• Mark every section that no longer matches how your agency operates
• Confirm or reassign the responsible person
• Update your risk assessment based on today's systems and threats
• Start collecting evidence now: training records, access reviews, and backup tests
• Put an annual review date on the calendar
Let's Make Your WISP Work for You
Main Event Managed Services works with independent insurance agencies across Wesley Chapel and the Tampa Bay area to build and maintain WISPs that reflect reality and hold up under scrutiny. If your WISP has not been opened since the day it was signed, visit maineventmsp.com and let's bring it back to life.